| DATE |
|
NAME |
INFO |
CATEGORIE |
WEB |
|
30.10.26 |
 |
Filter generation in practice: from algorithms to LLMs |
We automate filter generation for security alerts using an
algorithm, a large language model, and a group of LLM agents. |
AI |
SECURELIST |
|
29.10.26 |
 |
Apple Patches for October 2026 |
Apple today released patches for 304 vulnerabilties. This number
is still in line with prior Apple updates, and comes just about a month after
the last apple update. |
OS |
SANS |
|
29.10.26 |
 |
Unknown APT uses NetamLoader to attack a Win10 OS customized for
governments in Asia |
A couple of months ago,
our research revealed a highly sophisticated infection chain and a complex .NET
assembly-loading framework built on XAML markup, which strongly indicates a
supply-chain attack targeting a custom Windows build used exclusively by
government entities in Asia. The malicious framework has been labeled
NetamLoader; at present, no attribution to any known APT group has been
established. |
APT |
SECURELIST |
|
28.10.26 |
 |
Millions of security cameras at risk: DoS vulnerability in
Intelbras devices |
Network-connected
surveillance cameras are now widespread in both home and enterprise environments,
so securing them is essential to safeguarding physical spaces and sensitive
assets. As these devices continue to gain new features and network connectivity
capabilities, vulnerabilities in their implementation can have significant
security implications. |
Attack |
SECURELIST |
|
28.10.26 |
 |
An insecure neighbor: how a vulnerability chain led to an
isolation bypass in cloud infrastructure |
This article is published
for educational purposes only, to raise awareness among information security
professionals. The research was part of an official bug bounty program on a
major platform. We notified the cloud provider about the vulnerabilities in line
with our responsible disclosure policy, and all security issues we found were
fixed in full.
|
Security |
SECURELIST |
|
26.10.26 |
 |
Kali Linux 2026.3 |
We are back with Kali Linux 2026.3, the third release of the year!
We have been busy making it easier to build Kali, updating the desktop
experience, and bringing in more tools for you. Ready to get your hands on it?
Head over to the download page, or upgrade your existing installation to get
started. |
Security |
KALI |
|
26.10.26 |
|
Deploying AI agents securely: how Kaspersky products mitigate AI
threats |
AI agents and associated
tooling are becoming increasingly common in corporate infrastructure. Agents can
perform a range of actions with the user’s privileges, such as accessing data,
running commands, and interacting with external services. This creates new
security risks, especially when these tools are used without the security team’s
oversight or well-designed policies. |
AI |
SECURELIST |
|
22.10.26 |
|
How APT41 revived the BlackLotus bootkit to attack diplomatic
organizations in Central Asia |
Back in October 2022,
Kaspersky GReAT was looking into a peculiar advertisement on a hacking forum. A
cybercriminal
had been advertising a UEFI bootkit, dubbed BlackLotus, that could bypass
Secure Boot, for $5,000. Given the low price for such powerful capabilities, the
cybersecurity community initially took this advertisement with a grain of salt.
As no BlackLotus samples were found in the wild, no one could at the time verify
the claims made in the forum post. |
APT |
SECURELIST |
|
22.10.26 |
 |
Critical RCE vulnerabilities in PHP (CVE-2026-109618,
CVE-2026-109619) |
On October 20, 2026, the
PHP security team
published a preliminary notice regarding an upcoming emergency release that
addresses two critical vulnerabilities (both rated 9.2 on the CVSS scale). The
patches were released on Wednesday, October 21, 2026, at 14:00 UTC. |
Vulnerebility |
SECURELIST |
|
21.10.26 |
|
Operation FlashHole: Lazarus breaks security, defies control |
In January, we responded
to the Lazarus Group’s novel attack campaign against South Korea, which followed
last year’s
Operation SyncHole. In this new operation, the group employed an updated
malware chain that included both their old and new malware, which we disclosed
in full, and used another mandatory South Korean security software program as a
part of infection chain using a watering‑hole strategy. |
APT |
SECURELIST |
|
21 .10.26 |
|
The journey of a paper unicorn: adventures inside a modern
warehouse |
Imagine you’ve ordered a
small paper unicorn from an online marketplace. You clicked “Buy”, received a
cheerful notification, and expect a courier to bring the box tomorrow. If the
unicorn is delayed by a day, it will be annoying but not catastrophic: an
apology, a discount promo code — and the incident is forgotten. |
Security |
SECURELIST |
|
20.10.26 |
 |
ATT&CK v20 |
The October 2026 (v20) ATT&CK release updates Techniques, Groups, Campaigns and
Software for Enterprise, Mobile, and ICS. |
Security |
MITRE |
|
15.10.26 |
|
Orphaned VBA Projects Inside DWG Files |
Years ago I wrote
diary
entries
about VBA code stored inside AutoCAD drawing files (.dwg). |
Security |
SANS |
|
14.10.26 |
 |
October 2026 Microsoft Patch Tuesday |
Microsoft today released
patches for 1,417 vulnerabilities. 76 of these vulnerabilities are rated
critical, with 7 critical vulnerabiilties requiring no customer actions. One
vulnerability was disclosed before today's patch Tuesday, and one is already
exploited.CVE-2026-96951:
An already exploited Windows Shell Security Feature Bypass Vulnerability.
|
OS |
SANS |
|
13.10.26 |
 |
Auditing
the auditor: Unmasking Apex Accelerator |
REF8801 exposes how Apex Accelerator combines convincing Web3 services with
malicious npm packages, attacker-controlled AI infrastructure, and cross-platform
malware delivery.Elastic Security Labs identified a malicious npm package,
@apexacc/cli, which led us to an operation posing as a Web3 accelerator. |
Security |
Elastic Security Labs |
|
12.10.26 |
|
Never Deleted, Only Re-Pointed: Inside the 17,600-Repo FakeGit Fleet That
Re-Arms Overnight |
Around 06:30 UTC on October 4, a script started editing READMEs across FakeGit,
the network of fake GitHub repos that delivers the SmartLoader malware loader.
Over the next thirty-four hours, more than thirteen thousand GitHub repositories
were pushed in coordinated bursts, at up to 2,999 an hour. |
Hack |
APIIRO |
|
10.10.26 |
|
Scans for Atlassian vulnerablity (CVE-2026-21589) |
Atlassian published patches for
multiple products to fix an "Arbitrary File Access" vulnerability [CVE-2026-21589].
An attacker can read arbitrary files in the web application's directory,
potentially exposing sensitive information such as configuration files. |
Vulnerebility |
SANS |
|
10.10.26 |
|
More
RMM Tools In the Wild |
It seems that a trend started… I continue my
journey discovering more RMM ("Remote Management & Monitoring") tools abused by
threat actors! A few days ago, I wrote a diary[1]
about ScreenConnect used in the wild. Today, I found another one. |
Security |
SANS |
|
10.10.26 |
|
Reconstructing AI Agent Activity: Two New Scripts for Forensic
Review |
We just did a major update
to FOR577 and added a lot of new material on day 5 about investigating AI usage
in incident response. In the new material we dicsuss 8 of the most popular AI
coding assistants and agents including Claude Code, Codex, Gemini CLI, Cursor,
Copilot, Warp, Windsurf, and Qwen Code. |
AI |
SANS |
|
7.10.26 |
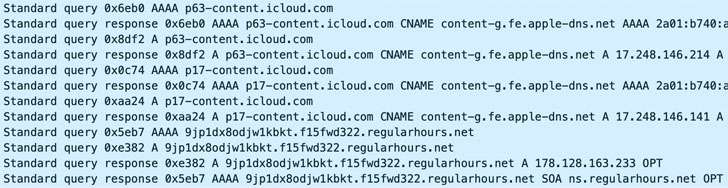 |
CrocoRat Adds a New Twist to ClickFix with DNS Payload
Delivery |
ClickFix campaigns have become one of the most effective ways to
turn a browser session into code execution. The technique is simple: show the
victim a fake verification page, place a command on the clipboard, and convince
them to paste it into the Windows Run dialog. |
Virus |
Flare |
|
7.10.26 |
 |
IronChain Ransomware Threatens Businesses with Permanent Data Loss and Costly
Downtime |
During Cybersecurity Awareness Month, ransomware remains one of the clearest
examples of how a cyber incident can become a business continuity issue.
IronChain shows why. It puts business-critical data at risk of permanent loss
and can bring operations to a halt. |
Ransom |
ANYRUN BLOG |
|
7.10.26 |
 |
More Shells Than a Seafood Buffet: Tracking Citrix NetScaler
Exploitation Activities (CVE-2026-88771) |
As
early as the beginning of September 2026, eSentire's
Threat Response Unit (TRU)
observed multiple threat actor clusters exploiting
CVE-2026-88771, a
zero-day vulnerability later disclosed in Citrix's September 27, 2026 security
bulletin
CTX697096. This blog
examines the distinct attack clusters identified by TRU and highlights the
tactics, techniques, and procedures observed across these intrusions. |
Exploit |
eSentire |
|
6.10.26 |
 |
ATOMIC MACOS (AMOS) STEALER INFECTION FROM MALICIOUS AD
IMPERSONATING CLAUDE CODE |
Zip files are password-protected. Of note, this site has a new password
scheme. For the password, see the "about" page of this website. |
MALWARE TRAFFICS |
MALWARE TRAFFIC |
|
6.10.26 |
|
User
Agent Strings Curiosities |
Sometimes I have to smile, or my interest is triggered, when I
review new User Agent Strings in the honeypot logs. |
Security |
SANS |
|
6.10.26 |
|
TTY Logs and the Data it Captures |
For an experiment, I created a script [1]
that parses and send the TTY logs collected from actors or bots activity that
run various commands after they successfully login the DShield sensor. Those TTY
logs are sent daily at the end of each day to the DShield SIEM [2]
to be correlated with all the data. |
Security |
SANS |
|
5.10.26 |
 |
UAC-0277: ClickFix on compromised websites to spread LUNEXSTEALER |
In
September 2026, CERT-UA specialists discovered over 100 compromised websites to
which malicious JavaScript code had been added by attackers. When visiting such
a site, the user was shown a fake Cloudflare verification page, which, under the
pretext of confirming that the visitor was a human, offered to execute a
command. Executing the command resulted in downloading and installing an MSI
package from a remote server (ClickFix technique). |
BATTLE OF UKRAINE |
BATTLE OF UKRAINE |
|
2.10.26 |
|
Gotta
breach 'em all! The journey of ShinyHunters |
ShinyHunters has outlasted forum
takedowns, multiple arrests, and its own founders' convictions. This report
traces six years of activity and tactical evolution. From stolen S3 buckets to
zero-day exploits, we attempted to explain why the brand keeps surviving what
should have ended it. |
APT |
SEKOIA |